

HTTP 200 verified twice
Finding your next stop…
Loading the latest directory information.
Loading the latest directory information.
Start here for the decision-making essentials: what Keeper Security does, who it is for, how it is accessed, and the first-party sources behind this profile.
See official pricing
Keeper Security provides a zero-trust platform for privileged access, secrets, passwords, connections, endpoints and databases. It features zero-knowledge encryption, FedRAMP High authorization, AI-powered threat detection, and 100+ integrations for federal and enterprise use.
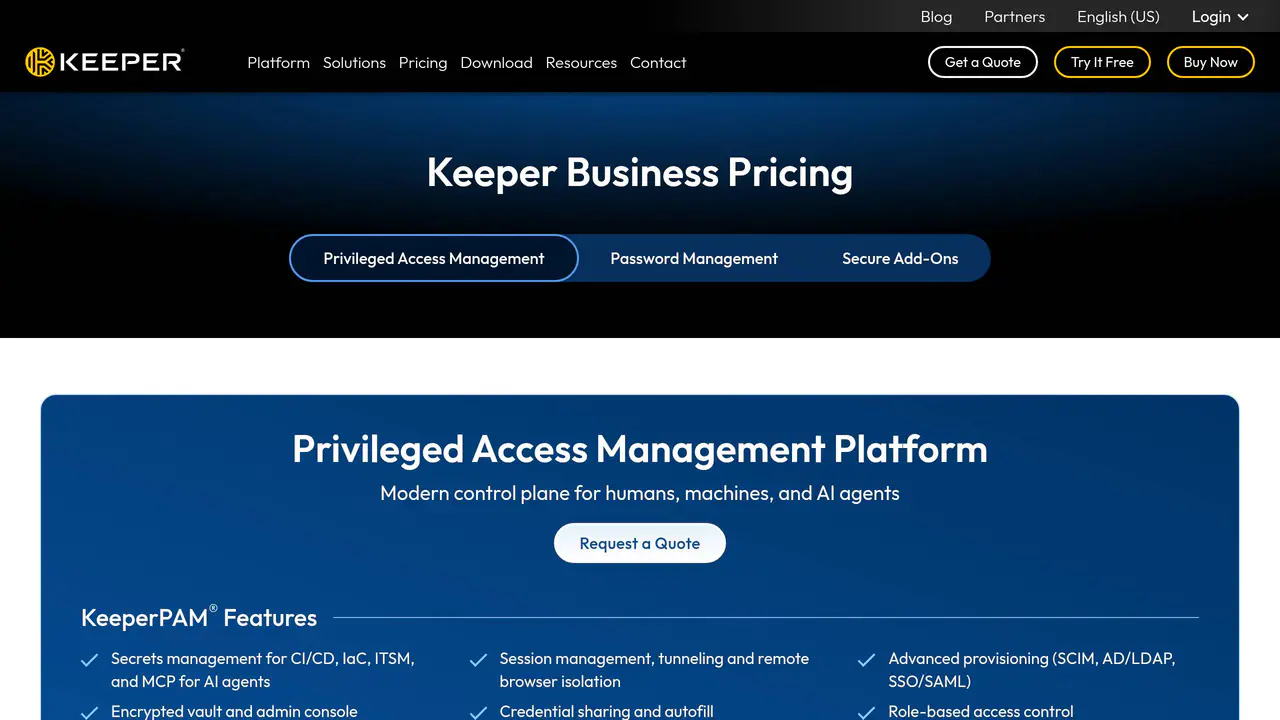
Read-only public captures of Keeper Security’s homepage and verified pricing page. Screenshots are dated, never live embeds, and open full-screen.
Short answers to the questions buyers and builders commonly ask about Keeper Security. Each answer cites the shared ledger below, where every source is listed once.
Unified zero-trust control plane for privileged access, secrets, remote connections, endpo · Zero-knowledge architecture with end-to-end encryption at the device and record levels · KeeperAI real-time AI-powered threat detection and response for PAM sessions · SDKs for Keeper Secrets Manager support Java/Kotlin, JavaScript, Python, .NET, Go, Ruby, a
Keeper is the unified control plane for privileged access, secrets, remote connections, endpoints and databases in a single zero-trust platform.
Millions of individuals and thousands of organizations
Trusted by millions of individuals and thousands of organizations
Secrets management for CI/CD, IaC, ITSM, and MCP for AI agents, plus password management, · Secure AI Agents · Secure Remote Database Access
Secrets management for CI/CD, IaC, ITSM, and MCP for AI agents
Keeper Admin API provides access to event logs, compliance data, reporting metrics, and ad · RESTful APIs for vault management, provisioning and audit logging, with Keeper Commander C · Developer SDKs and REST API for DevOps, IT security and software development teams, plus C · Keeper Commander CLI for scripting and scheduling recurring compliance reports and integra
The Keeper Admin API provides access to event logs, compliance data, reporting metrics and administrative insights via a flexible REST API interface.
Over 100 technology integrations including SSO Connect, Azure, SCIM, AD/LDAP, SSO/SAML, Co · Native integrations with CI/CD platforms, container environments, and orchestration tools · Keeper Agent Kit enables AI assistants (Claude Code, Codex, Cursor, GitHub Copilot) to acc · Keeper SSO Connect with Okta, Microsoft Entra ID, Ping Identity, Google Workspace, OneLogi
Over 100 technology integrations
Cloud-first identity security platform exceeding government standards for federal agencies · Keeper Commander can be deployed as a self-hosted REST API service that preserves zero-kno · Cloud and on-premises deployment supported via Keeper SSO Connect and Keeper SSO Connect C · Privileged access management deploys in minutes
The cloud-first identity security solution that exceeds stringent government standards for federal agencies.
This profile connects the jobs Keeper Security is described as handling with its delivery model, access options and the subjects used to match it to related products in this directory.
Each fact points to a recorded source, making it easy to distinguish verified product information from claims that need checking.
HTTP 200 verified twice
Keeper Security | Identity Security for Humans, Machines and AI Agents
Unified zero-trust control plane for privileged access, secrets, remote connections, endpo · Zero-knowledge architecture with encryption and decryption at the device and record levels · KeeperAI real-time threat detection that terminates high-risk sessions
Unified zero-trust control plane for privileged access, secrets, remote connections, endpoints and databases
Zero-knowledge architecture with end-to-end encryption at the device and record levels
KeeperAI real-time AI-powered threat detection and response for PAM sessions
Keeper Security, Inc.
FedRAMP High Authorized, GovRAMP High Authorized, FIPS 140-3 validated, ISO 27001/27017/27018 certified, PCI DSS certified, TrustArc privacy certified
Cloud-first identity security platform exceeding government standards for federal agencies
Over 100 technology integrations including SSO Connect, Azure, SCIM, AD/LDAP, SSO/SAML, Commander SDK, and CI/CD, IaC, ITSM, and MCP connectors
Secrets management for CI/CD, IaC, ITSM, and MCP for AI agents, plus password management, PAM, endpoint privilege management, database management, session management, tunneling, and remote browser isolation
A concise view of the jobs, capabilities and integrations described in the recorded product sources.
Documented product formats, platforms and official distribution destinations. Availability can vary by region and plan.
A concise history of software releases and material product changes. Events appear only when a dated source supports what changed.
Showing the newest updates and meaningful milestones. Open an entry for its summary and source.
Keeper published a blog post titled 'Top 7 Privileged Access Management Solutions,' originally dated September 10, 2025 and updated January 2, 2026, ranking PAM tools including its own offerings.
View source [19]Keeper Security announced that KeeperPAM was named a top-rated Privileged Access Management solution in a 2025 EMA report, highlighting industry analyst recognition of the platform.
View source [7]Keeper Security announced that KeeperPAM was recognized as the top-rated Privileged Access Management solution in Enterprise Management Associates' 2025 PAM report.
View source [7]Keeper announced its KeeperPAM platform was named a top-rated Privileged Access Management solution in Enterprise Management Associates' 2025 report.
View source [7]Keeper Security announced that KeeperPAM was named a top-rated Privileged Access Management solution in the 2025 EMA Report, citing industry recognition of its PAM capabilities.
View source [7]Facts, answers, structured details, milestones and primary resource links cite this shared ledger. Each external page appears once; release tags from the same GitHub project are grouped under one release history.
These tools share a workflow, capability or audience with Keeper Security. They may complement it rather than replace it, and are not presented as integrations or endorsements.
Continuously validated by third-party security experts through penetration testing, bug bounties, and a public vulnerability disclosure program
SDKs for Keeper Secrets Manager support Java/Kotlin, JavaScript, Python, .NET, Go, Ruby, and Rust
Keeper Secrets Manager supports secure secret access for AI agents via the Model Context Protocol (MCP)
Zero-knowledge, zero-trust security: secrets are never written to disk by default and are held in memory only for the duration of the process
KeeperDB runs as a standalone desktop app on Windows, macOS, and Linux, and is also offered as a VS Code extension and browser extensions (Chrome, Firefox, Safari, Edge, Opera)
Native integrations with CI/CD platforms, container environments, and orchestration tools including Kubernetes, plus a Terraform Provider
Keeper Commander can be deployed as a self-hosted REST API service that preserves zero-knowledge encryption
Keeper Admin API provides access to event logs, compliance data, reporting metrics, and administrative insights via a REST API; additional APIs include Account Management API for MSPs, Family Provisioning API, Student Provisioning API, and
SCIM 2.0 for automated user provisioning, deprovisioning, group management, shared folder access, and policy enforcement
24x7 support is available, with priority email, live chat, phone support, and enterprise onboarding help for Business & Enterprise customers, and a dedicated partner team for MSPs
Keeper SSH Key Management centralizes SSH key storage, access control, and lifecycle with automated rotation, RBAC, audit logging, and browser-based access (no VPN required)
KeeperDB connects to PostgreSQL, MySQL, SQLite, Microsoft SQL Server, Oracle, and Amazon Redshift with a query editor, SQL autocomplete, schema graph, real-time monitor, and KeeperAI assistant
Keeper's connection management solutions are commercially supported capabilities powered by Apache Guacamole, developed by its original creators
FIPS 140-3 validated, certified by the NIST Cryptographic Module Verification Program (CMVP)
Quarterly third-party penetration testing by NCC Group, CyberTest and independent security researchers against all solutions and systems
Vulnerability Disclosure Program (VDP) and bug bounty program managed by Bugcrowd
Vault data at rest encrypted locally on the user's device with AES-256 GCM; data in transit encrypted with TLS 1.3 plus an additional payload encryption layer
Supports multi-factor authentication (MFA), SSO authentication, conditional access policies (CAP), FIDO2 WebAuthn hardware security keys, passkeys, biometric login (Face ID, Touch ID, Windows Hello) and Keeper DNA smartwatch-based MFA
Rollout of Quantum-Resistant Cryptography (QRC) as an additional encryption wrapper on the transmission key started in Q1 2026
Super-encryption performed using multi-region hardware security modules (HSM) with non-exportable keys on top of device-encrypted ciphertext stored in AWS
Keeper Enterprise Password Management (EPM) gives IT admins visibility and control over employee password practices and security enforcement
Keeper Secrets Manager (KSM) manages infrastructure secrets, SSH keys, API keys and certificates with SDKs and CI/CD integration for engineering teams
Keeper Connection Manager (KCM) is a browser-based Zero-Trust Network Access (ZTNA) remote desktop gateway to RDP, SSH, databases, internal web apps and Kubernetes endpoints with no agent required
Keeper Security, Inc.
Most extensible password management platform for enterprises
Keeper Agent Kit enables AI assistants (Claude Code, Codex, Cursor, GitHub Copilot) to access Keeper Secrets Manager via natural language prompts
Model Context Protocol (MCP) integration via Docker or Node.js implementations
Keeper SSO Connect with Okta, Microsoft Entra ID, Ping Identity, Google Workspace, OneLogin, Auth0, AWS SSO, and SAML 2.0
SCIM provisioning with Microsoft ADFS, Thales SafeNet Trusted Access, RSA SecurID Access, Rippling, Shibboleth, and others