HTTP 200 verified twice
Finding your next stop…
Loading the latest directory information.
Loading the latest directory information.
Start here for the decision-making essentials: what FireMon does, who it is for, how it is accessed, and the first-party sources behind this profile.
Tailored/customized pricing
every deployment starts with Security Manager core platform p
FireMon is a network security policy management platform that centralizes and automates firewall, cloud, and microsegmentation policy across 120+ vendors. Trusted by 1,700+ organizations in 70+ countries, it reduces exposure, accelerates change, and provides continuous compliance reporting.
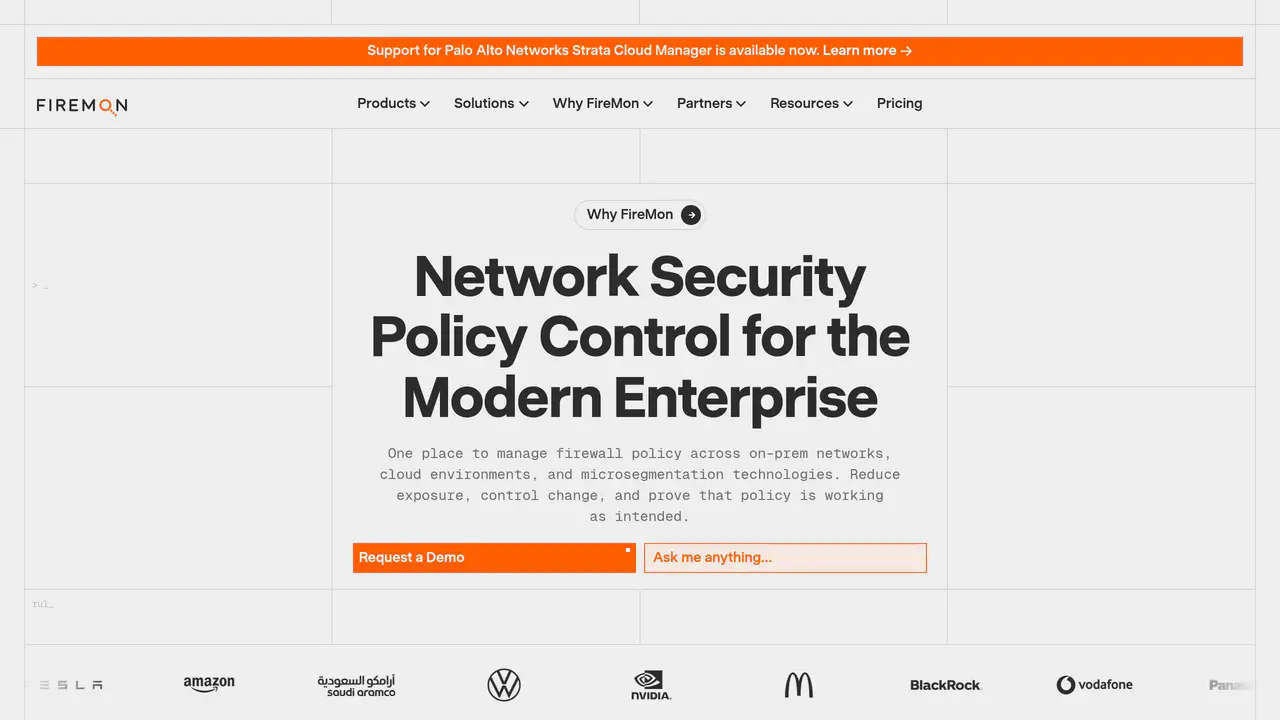
Read-only public captures of FireMon’s homepage. Screenshots are dated, never live embeds, and open full-screen.
Short answers to the questions buyers and builders commonly ask about FireMon. Each answer cites the shared ledger below, where every source is listed once.
Analyze, detect, and mitigate policy-related vulnerabilities; improve speed and cost of po · Network security policy management across multi-vendor firewalls, cloud, and segmentation · Automatically ingests and normalizes configurations from 120+ firewall and cloud platforms · API-first architecture for custom integrations
Analyze, detect, and mitigate policy-related vulnerabilities that could expose the organization to outages or attacks.
Enterprise security teams managing hybrid, multi-vendor firewall environments; trusted by · Telecommunications providers (7 of the Top 10 Telecom Companies use FireMon)
Trusted by 1,700+ organizations.
Hybrid enterprise firewall policy management across on-premises, virtual, and cloud networ · Microsegmentation governance for north-south and east-west traffic · Firewall and network security policy management across hybrid IT environments · Healthcare network security with HIPAA audit readiness and segmentation across hospitals,
Manage rules, validate changes, reduce risky access, and prove compliance across on-premises, virtual, and cloud network controls.
Does not detect or block AI-driven attacks directly; focused on reducing the policy weakne
FireMon does not detect or block AI attacks directly. It helps your team reduce the policy weaknesses those attacks can exploit.
Tailored/customized pricing; every deployment starts with Security Manager core platform p
FireMon pricing is tailored to your environment, starting with Security Manager and optional modules for automation, risk, visibility, and compliance.
API-first architecture enables custom integrations
API-first architecture enables custom integrations.
This profile connects the jobs FireMon is described as handling with its delivery model, access options and the subjects used to match it to related products in this directory.
Each fact points to a recorded source, making it easy to distinguish verified product information from claims that need checking.
HTTP 200 verified twice
FireMon | Network Security Policy Control
Invented the Network Security Policy Management category · Founded by Jody Brazil, who still leads as CEO today · Trusted by 1,700+ organizations across 70+ countries
Network security policy management control plane platform across firewalls, cloud, and microsegmentation
Analyze, detect, and mitigate policy-related vulnerabilities; improve speed and cost of policy changes; achieve and maintain network security policy compliance
Hybrid cloud deployment spanning on-premises, virtual, and cloud network controls
Connects policy management across more than 120 supported firewall, cloud, network, microsegmentation, and workflow technologies
Enterprise security teams managing hybrid, multi-vendor firewall environments; trusted by 1,700+ organizations
FireMon, LLC
Jody Brazil is Founder & CEO
Tailored/customized pricing; every deployment starts with Security Manager core platform plus optional modules for automation, risk, visibility, and compliance
Support via support@firemon.com plus a support hub for documentation and knowledge
A concise view of the jobs, capabilities and integrations described in the recorded product sources.
Documented product formats, platforms and official distribution destinations. Availability can vary by region and plan.
A concise history of software releases and material product changes. Events appear only when a dated source supports what changed.
Showing the newest updates and meaningful milestones. Open an entry for its summary and source.
FireMon announced completed product integration with Palo Alto Networks Strata Cloud Manager, bringing cloud-managed policy and configuration data into FireMon for policy ingestion, normalization, analysis, risk validation and governance workflows.
View source [9]FireMon announced completion of its product integration with Palo Alto Networks Strata Cloud Manager, enabling joint customers to bring policy and configuration information from Palo Alto cloud-managed environments into FireMon for policy control, analysis, ri
View source [9]FireMon and Illumio announced general availability of a joint Zero Trust Control Plane for hybrid enterprises, extending Zero Trust beyond application visibility into continuous, governed control of segmentation across network, cloud, and host environments.
View source [13]FireMon announced a partnership with Illumio to deliver what it describes as the first Zero Trust control plane, extending Zero Trust beyond application visibility to continuous, governed control of segmentation across network, cloud, and host environments.
View source [13]FireMon and Illumio announced general availability of an integrated Zero Trust control plane that extends governed, continuous segmentation policy across network, cloud, and host environments.
View source [13]Facts, answers, structured details, milestones and primary resource links cite this shared ledger. Each external page appears once; release tags from the same GitHub project are grouped under one release history.
These tools share a workflow, capability or audience with FireMon. They may complement it rather than replace it, and are not presented as integrations or endorsements.
Personal information stored on secure servers behind firewalls with SSL-encrypted transactions
Help security teams reduce exposure, support critical applications, respond to change, and produce defensible evidence for auditors across hybrid networks
Network security policy management across multi-vendor firewalls, cloud, and segmentation
Automatically ingests and normalizes configurations from 120+ firewall and cloud platforms into a unified data model
API-first architecture for custom integrations
Modules include Policy Planner for change automation, Policy Optimizer for cleanup, Risk Analyzer for risk scoring, and Insights AI for analytics
Hybrid enterprise firewall policy management across on-premises, virtual, and cloud network controls
Microsegmentation governance for north-south and east-west traffic
Centralized policy database spanning on-prem firewalls, cloud security groups, and microsegmentation platforms
Supports Check Point, Cisco, Palo Alto Networks, Fortinet firewalls, AWS cloud, and leading microsegmentation tools
Available integration with Palo Alto Networks Strata Cloud Manager for policy ingestion, normalization and analysis
Founded by Jody Brazil, who still leads as CEO today
Invented the Network Security Policy Management category
Serves enterprise customers across 70+ countries
Continuous, automated firewall policy compliance monitoring with real-time violation detection and audit-ready reports
Firewall and network security policy management across hybrid IT environments
Telecommunications providers (7 of the Top 10 Telecom Companies use FireMon)
120+ firewall and cloud platforms supported
Cisco, Palo Alto, Fortinet, Check Point, Juniper, F5, AWS, Azure, Google Cloud, SD-WAN, and 5G infrastructure tools
Verified to support 15,000+ devices and 25M+ rules in production with high availability and distributed architecture options
Most telecom providers achieve initial visibility in 2–4 weeks; full deployment with automation typically takes 2–3 months
ServiceNow, Jira, SIEM platforms (Splunk, QRadar), SOAR solutions, vulnerability scanners, and cloud platforms
API-first architecture enables custom integrations
PCI DSS, NIST 800-53, GDPR, HIPAA, SOX, NERC CIP, DORA, and CSA supported out of the box
Vendor-agnostic policy model that normalizes multi-vendor firewalls, cloud platforms, and network devices into one data layer
Does not detect or block AI-driven attacks directly; focused on reducing the policy weaknesses those attacks can exploit
FireMon
Network security policy management platform for firewall and cloud environments