
HTTP 200 verified twice
Finding your next stop…
Loading the latest directory information.
Loading the latest directory information.
Start here for the decision-making essentials: what CyCognito does, who it is for, how it is accessed, and the first-party sources behind this profile.
Custom quote — pricing varies based on customer needs, services selected, number of extern
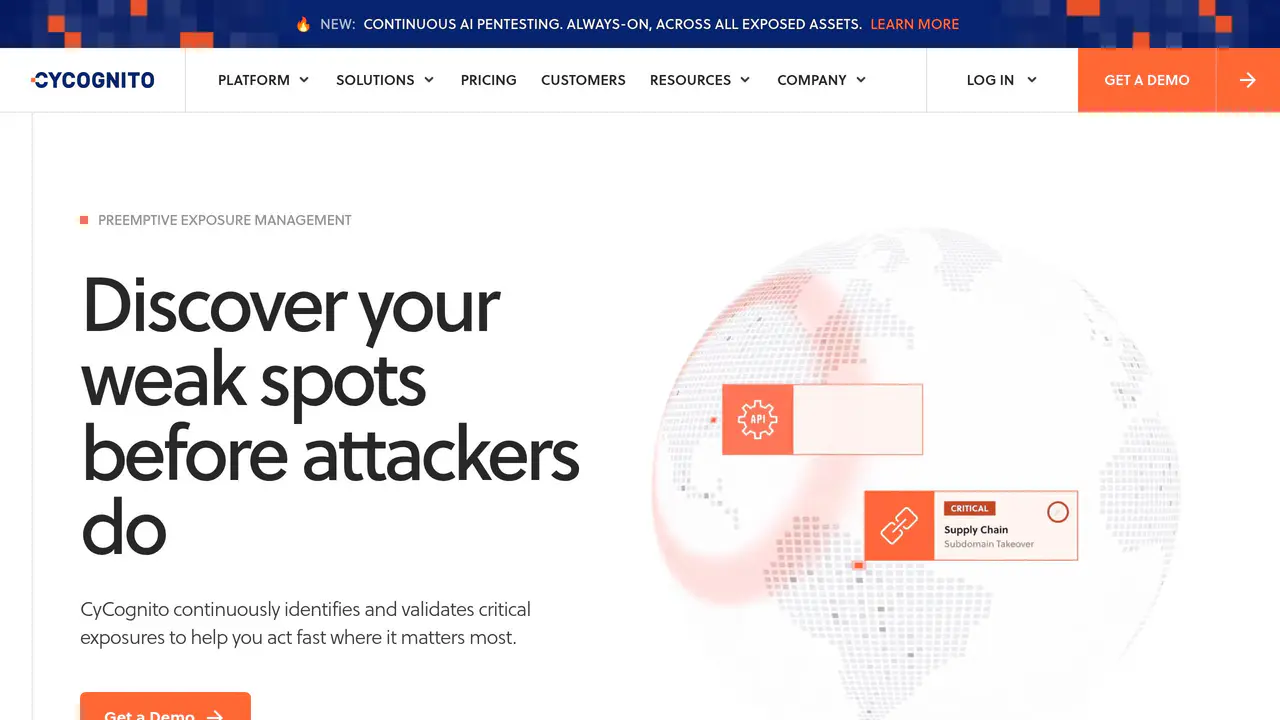
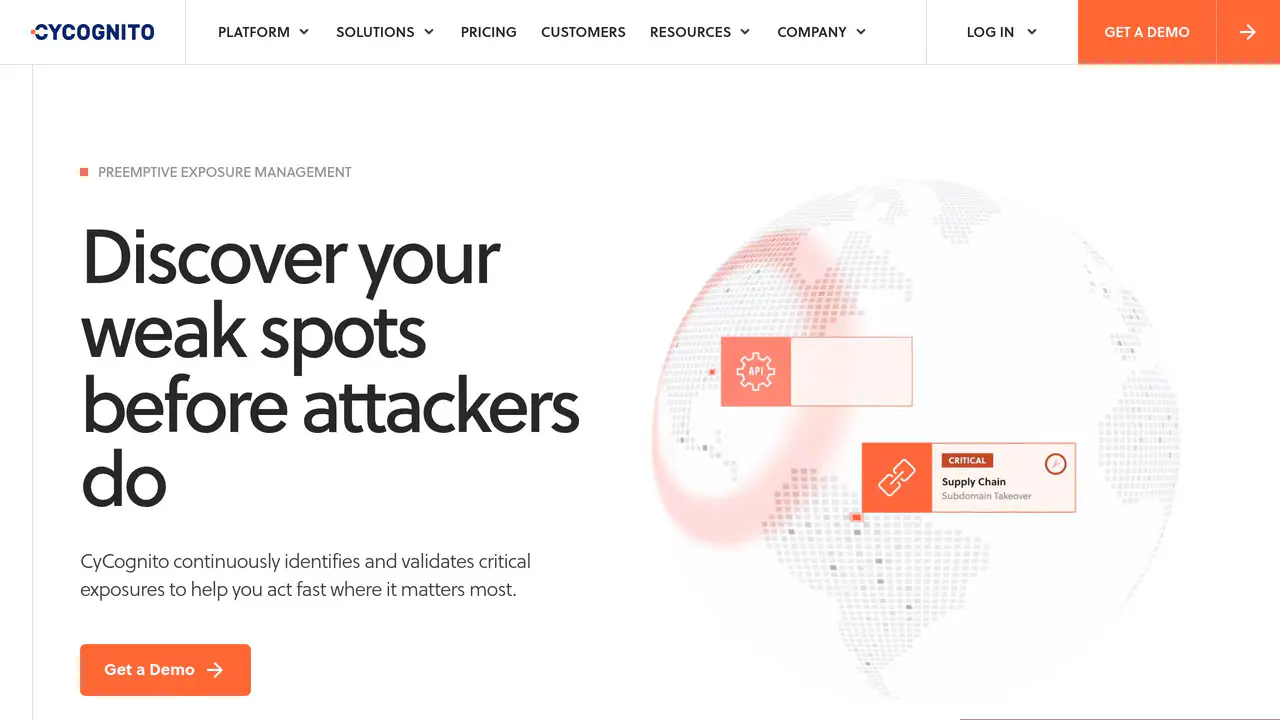
CyCognito continuously identifies and validates critical exposures to help you act fast where it matters most.
Read-only public captures of CyCognito’s homepage and verified pricing page. Screenshots are dated, never live embeds, and open full-screen.
Short answers to the questions buyers and builders commonly ask about CyCognito. Each answer cites the shared ledger below, where every source is listed once.
External Attack Surface Management (ASM) with continuous asset discovery, DAST, vulnerabil · Continuous asset discovery, contextualization, and security testing for external attack su · External Attack Surface Management platform · Risk-based prioritization with active validation for Unified Vulnerability Management
Industry's only full-scale autonomous testing, scaling to millions of apps or devices and running continuously, with no setup required.
Leading global enterprises · Leading global enterprises and IT security and operations teams · Emerging companies, government agencies and Fortune 500 organizations
Trusted by leading global enterprises.
Preemptive exposure management and Continuous Threat Exposure Management (CTEM), including · External attack surface management (ASM) and exposure management, including asset discover · Unified Vulnerability Management (UVM) · External attack surface investigation during incident response (e.g., Log4j response plann
CTEM is what ties the platform together: a continuous loop that moves from diagnosing exposure to acting on it, then starts again.
Custom quote — pricing varies based on customer needs, services selected, number of extern
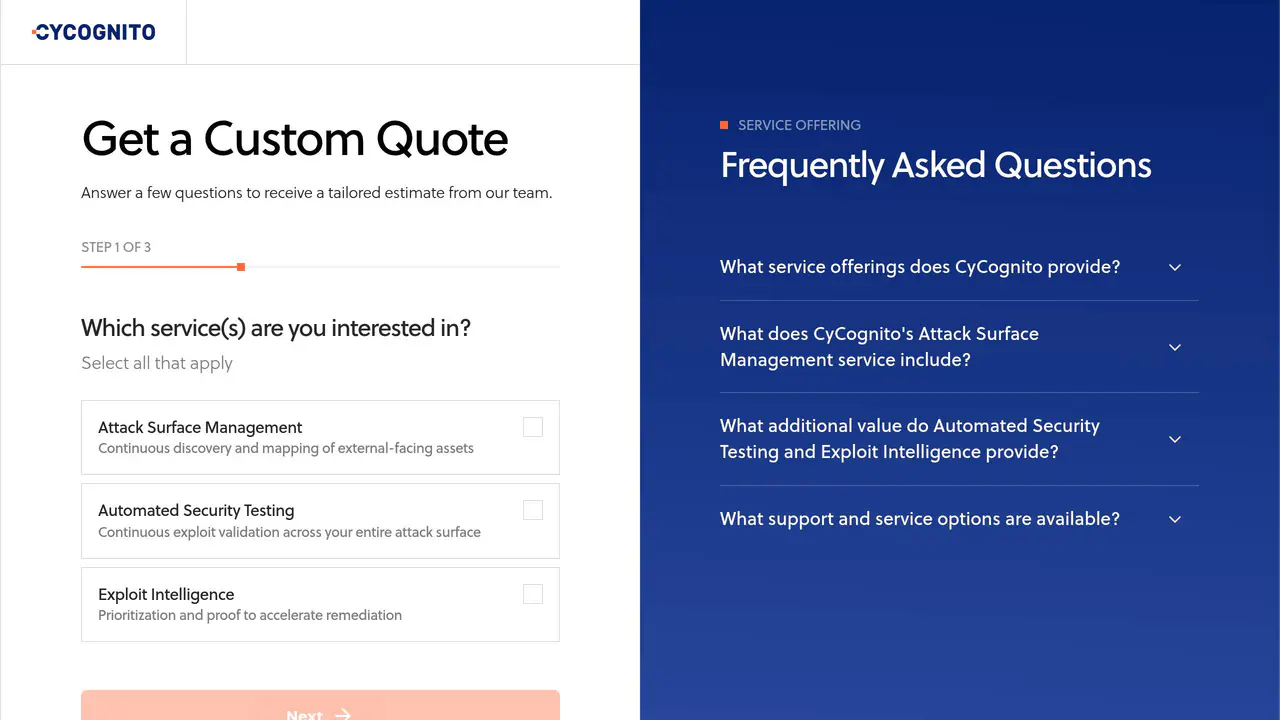
Get a Custom Quote
ServiceNow (for delegating remediation tasks and tracking fixes across security, IT, and b · Supports 1,200+ integrations connecting exposure data to SIEM, SOAR, ticketing, cyber asse · Integrates with Splunk for asset and vulnerability data streaming to reduce MTTR for SecOp · Integrates with ServiceNow Vulnerability Response to push findings for contextualization a
Identify asset owners to delegate tasks and track fixes across integrated security, IT, and business platforms (e.g., ServiceNow).
Cloud/SaaS — no asset lists or setup needed; autonomous scanning with daily scan cadence · External exposure management deployment model
No asset lists or setup needed.
This profile connects the jobs CyCognito is described as handling with its delivery model, access options and the subjects used to match it to related products in this directory.
Each fact points to a recorded source, making it easy to distinguish verified product information from claims that need checking.
HTTP 200 verified twice
Preemptive Exposure Management | ASM Leader | CyCognito
Company name: CyCognito · Founded in 2017 · Headquartered at 3000 El Camino Real, Palo Alto, California, US (94306)
CyCognito
2017
Palo Alto, California, US (3000 El Camino Real, Building 4, 2nd Floor Suite 200, 94306)
External Attack Surface Management (ASM) with continuous asset discovery, DAST, vulnerability scanning, and autonomous security testing
Preemptive exposure management and Continuous Threat Exposure Management (CTEM), including CAASM gap closure, CNAPP coverage validation, and WAF/API security validation
Leading global enterprises
Cybersecurity SaaS platform — recognized as a Leader and Outperformer in the 2026 GigaOm Radar for ASM (out of 32 vendors)
Custom quote — pricing varies based on customer needs, services selected, number of external assets managed, and scan/test frequency
ServiceNow (for delegating remediation tasks and tracking fixes across security, IT, and business platforms)
A concise view of the jobs, capabilities and integrations described in the recorded product sources.
Documented product formats, platforms and official distribution destinations. Availability can vary by region and plan.
A concise history of software releases and material product changes. Events appear only when a dated source supports what changed.
Showing the newest updates and meaningful milestones. Open an entry for its summary and source.
CyCognito published a perspective article arguing that Continuous Threat Exposure Management reframes security metrics from activity counts toward impact-driven, validated-issue remediation.
View source [12]CyCognito published February 2026 platform updates focused on improving posture visibility, expanding in-app user learning, and streamlining asset and issue review.
View source [12]CyCognito published its February 2026 platform update covering posture visibility improvements, in-app user learning, and streamlined asset and issue review workflows.
View source [12]Facts, answers, structured details, milestones and primary resource links cite this shared ledger. Each external page appears once; release tags from the same GitHub project are grouped under one release history.
These tools share a workflow, capability or audience with CyCognito. They may complement it rather than replace it, and are not presented as integrations or endorsements.
Cloud/SaaS — no asset lists or setup needed; autonomous scanning with daily scan cadence
LinkedIn (cycognito), Crunchbase, Facebook (/CyCognito/), Glassdoor, GitHub (CyCognito), Twitter (@CyCognito)
Continuously identify and validate critical exposures to help organizations act fast where it matters most, enabling a shift from 'what we have' to 'what matters now'
Continuous asset discovery, contextualization, and security testing for external attack surfaces
External attack surface management (ASM) and exposure management, including asset discovery, vulnerability detection, risk scoring, and attack path analysis
Leading global enterprises and IT security and operations teams
Supports 1,200+ integrations connecting exposure data to SIEM, SOAR, ticketing, cyber asset inventory, and cloud security tools
Integrates with Splunk for asset and vulnerability data streaming to reduce MTTR for SecOps
Integrates with ServiceNow Vulnerability Response to push findings for contextualization and remediation
Integrates with Jira to automatically open and update tickets when new issues are surfaced
Integrates with PagerDuty to trigger incidents from critical findings
Integrates with cloud security, CAASM, and vulnerability management platforms including Wiz, Axonius, JupiterOne, CrowdStrike, Qualys, Rapid7, Tenable, and Cortex XDR
SOC 2 Type II attested; the report is an independent auditor's attestation of security controls covering security, processing integrity, confidentiality, and data privacy per AICPA standards
ISO 27001 certified, demonstrating adherence to international standards for an information security management system
GDPR-compliant; processes personal data collected for account creation and platform access in accordance with the EU GDPR
External Attack Surface Management platform
Risk-based prioritization with active validation for Unified Vulnerability Management
Outside-in discovery of external assets including shadow IT, shadow AI, and other 'unknown unknowns'
Outside-in mapping of the external attack surface to reveal assets and access paths attackers can reach
Active validation of which vulnerability findings are actually exploitable
Attack-path mapping to break multi-step attack chains and reduce MTTR
Continuous attacker-side testing that replaces point-in-time assessments
Continuous AI pentesting using AI agents across the full external surface
Two testing modules — one passive and one active
Unified Vulnerability Management (UVM)
External attack surface investigation during incident response (e.g., Log4j response planning)
Leading global enterprises
Reduces 'critical' findings from about 25% to 0.1% or less by combining exploitability, business context, and threat intelligence